SM Entertainment Gets Hacked: 7 Shocking Details About the Private Information Leak
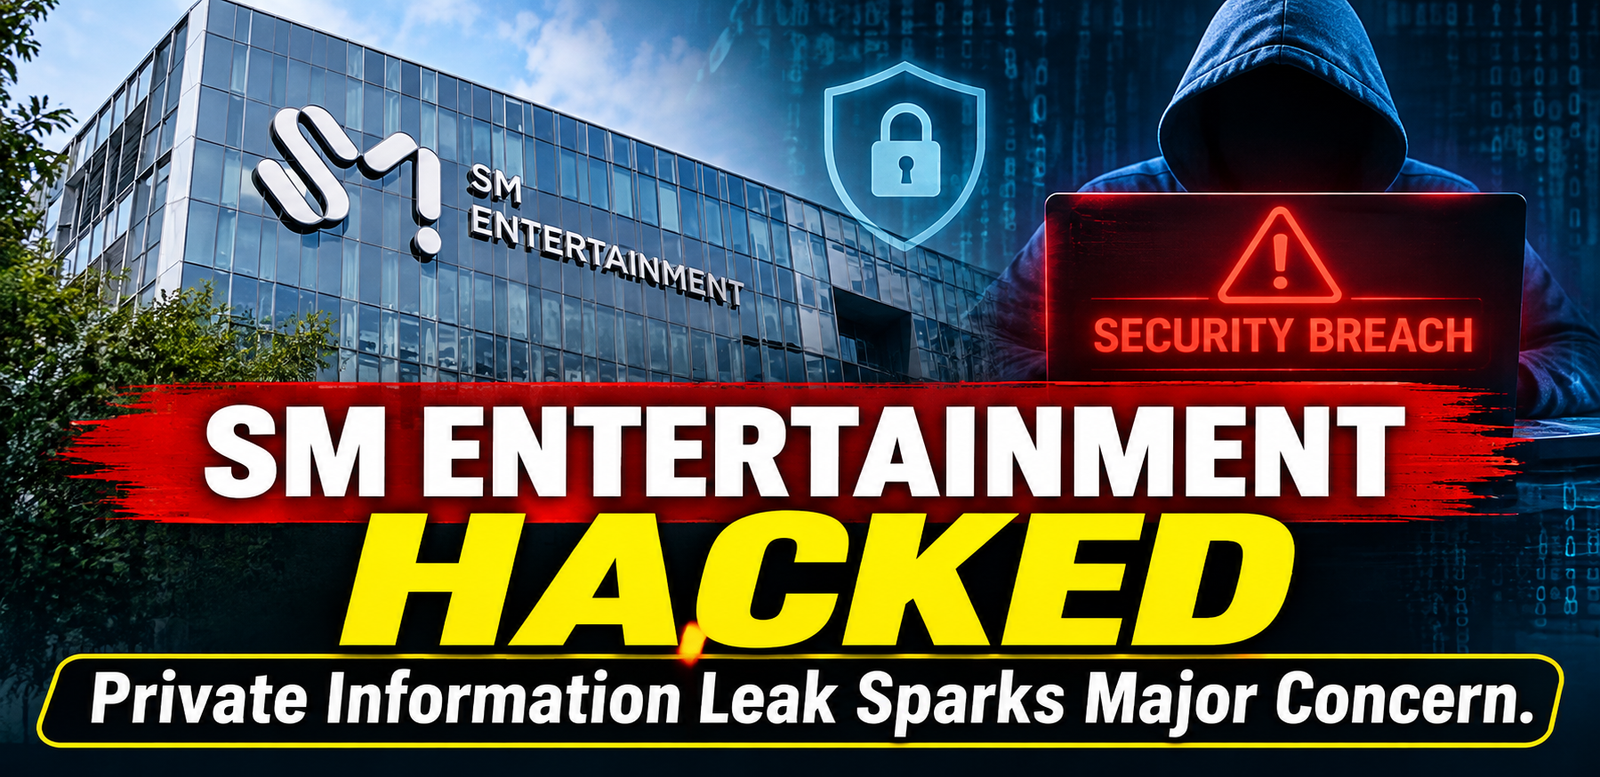
The K-pop entertainment industry is facing another serious cybersecurity concern after SM Entertainment confirmed that an external attacker accessed its internal business systems and leaked confidential documents.
The incident became public on November 8, 2026, when the South Korean entertainment company published an official notice and apologized for the situation. According to the company’s announcement, the security breach happened around November 4.
The leaked information reportedly included names, mobile phone numbers, home addresses, bank account numbers, South Korean resident registration numbers, employee positions, and details recorded in certain contracts.
The situation has also attracted attention because two SM Entertainment affiliates, DearU and Dream Maker Entertainment, experienced similar information leaks.
However, one important detail needs clarification: SM’s reporting indicated that employee and business-related information was exposed, while DearU said its Bubble fan-service users’ personal information wasn’t affected.
The SM Entertainment hacked incident has therefore raised important questions about employee privacy, company security, and the protection of personal information in the Korean entertainment industry.
Here are seven important details about what happened, what information was exposed, and what the company has said so far.
What Happened to SM Entertainment? Understanding the Hacking Incident
SM Entertainment is one of South Korea’s most influential entertainment companies. It manages and works with several popular K-pop artists and groups, making its business operations an important part of the Korean music industry.
On November 8, 2026, the company released an official announcement confirming that an external attacker had gained unauthorized access to its internal business systems.
According to the announcement, the attacker accessed systems that included the company’s electronic approval platform. Some documents stored within those systems were then transferred outside the company.
This wasn’t simply a case of someone accessing a public website. The incident involved internal business information, which makes the situation more serious.
SM Entertainment confirmed that it was investigating the circumstances with relevant authorities.
The company also apologized to those who might have been affected.
Table of Contents
How Was the Attack Discovered?
SM Entertainment said its internal security monitoring process helped identify the unauthorized access.
After discovering the incident, the company took immediate steps to stop further access.
These included:
- Blocking the IP addresses used in the attack.
- Blocking the identified access routes.
- Replacing unauthorized access keys.
- Working with government authorities.
- Cooperating with external cybersecurity specialists.
- Reviewing its internal security systems.
However, the company hasn’t publicly disclosed the complete technical details of the attack.
It’s also important to understand that identifying unauthorized access doesn’t automatically reveal who carried out the attack or exactly how the attacker entered the system.
Those details require further investigation.
When Did the SM Entertainment Hacking Incident Happen?
According to SM Entertainment’s official notice, the personal information leak occurred around November 4, 2026.
The company publicly acknowledged the incident on November 8.
This means there was a gap between the reported breach and the public announcement.
During that period, the company identified the unauthorized access, blocked the known access routes, and began taking steps to investigate the incident.
Here’s a timeline of the confirmed developments.
| Date | Important development |
|---|---|
| November 4, 2026 | Approximate date of the reported information leak |
| November 8, 2026 | SM Entertainment publicly acknowledged the breach |
| November 8, 2026 | The company issued an apology and security guidance |
| November 9, 2026 | Further reporting highlighted the impact on SM and its affiliates |
| Ongoing | Investigation, affected-person notifications, and security reviews |
The exact time when the attacker first gained access hasn’t been publicly established.
Similarly, the total number of affected people and the number of documents taken haven’t been confirmed in the available announcements.
7 Shocking Details About the SM Entertainment Data Breach
The incident has attracted significant attention because it involves more than ordinary business documents.
Here are seven important developments readers should understand.
1. An External Attacker Accessed SM Entertainment’s Internal Systems
The first major detail is that the company confirmed unauthorized access to its internal business systems.
SM Entertainment specifically mentioned its electronic approval system.
Such systems are commonly used by businesses to manage internal documents, approvals, and administrative processes.
They can contain information that isn’t intended for public access.
The attacker reportedly obtained some documents stored within the company’s systems and transferred them externally.
SM hasn’t confirmed the exact vulnerability or technical method used to gain access.
Therefore, claims about a particular hacking technique or security weakness should be treated cautiously until the investigation provides more information.
2. Employee Personal Information Was Exposed
One of the most concerning aspects of the incident is the exposure of personal information.
According to SM Entertainment, the leaked information included several categories of personal data.
These reportedly included:
- Names.
- Mobile phone numbers.
- Residential addresses.
- Bank account numbers.
- South Korean resident registration numbers.
- Department and job-position information.
- Certain details included in contracts.
Not every affected individual necessarily had all these details exposed.
SM explained that the information involved differs from person to person.
The company was working to identify the affected individuals and notify them individually through email or text messages.
This is particularly important because personal information can be misused even when passwords or social media accounts aren’t directly involved.
3. Sensitive Financial and Identification Details Were Involved
The exposure of bank account numbers and resident registration numbers has increased concerns about possible identity-related fraud.
In South Korea, resident registration numbers are important personal identification details.
If such information falls into the wrong hands, affected individuals may face increased risks of impersonation or fraudulent attempts.
Bank account information can also make targeted financial scams more convincing.
However, it’s important not to confuse the possibility of misuse with confirmed financial crime.
As of the company’s announcement, SM said it hadn’t identified cases of secondary damage caused by the leaked information.
The company nevertheless warned people to remain alert.
4. DearU, the Company Behind Bubble, Was Also Affected
Another important development involves DearU, the company operating the popular Bubble fan communication platform.
Bubble allows fans to communicate with participating artists through a subscription-based messaging service.
The platform is associated with several K-pop artists, which naturally raised questions among fans after reports of the security incident emerged.
However, there’s an important distinction.
According to SM’s explanation and reporting by SBS, DearU experienced a separate employee-related information leak, but Bubble users’ personal information wasn’t reported as compromised.
This means fans shouldn’t automatically assume their Bubble conversations, subscription details, or personal accounts were exposed.
DearU’s reported employee information exposure and the security of Bubble’s fan accounts are two different matters.
For now, readers should rely on official updates rather than unverified social media claims.
5. Dream Maker Entertainment Also Experienced a Data Leak
The incident wasn’t limited to SM Entertainment and DearU.
Dream Maker Entertainment, a concert production affiliate, also experienced a similar personal information leak.
This development has raised broader concerns about information security across the company’s business network.
Entertainment companies handle many types of confidential records, including:
- Employee information.
- Business partner details.
- Administrative documents.
- Contract records.
- Financial and operational information.
Concert production companies also work with multiple external partners, suppliers, and business organizations.
However, the available information doesn’t establish that every category of business information or every partner’s records was exposed.
The full impact remains subject to investigation.
6. SM Entertainment Issued an Official Apology
SM Entertainment publicly acknowledged the incident and apologized to people who may have been affected.
The company said it was treating the matter seriously.
It also confirmed that it was cooperating with relevant authorities to investigate the exact circumstances.
An important part of its response was the decision to notify affected individuals individually.
This matters because people need to understand whether their particular information was exposed.
A general announcement cannot explain the exact information involved for every person.
The company therefore said it would provide notifications through email or text messages as it identified the affected individuals.
7. The Company Warned About Phishing and Financial Scams
Perhaps the most important practical warning concerns possible secondary misuse.
SM Entertainment specifically advised people to be careful about suspicious calls, messages, and emails.
Scammers may impersonate company representatives or other trusted contacts.
They may claim they need to verify personal information, confirm bank details, or arrange compensation.
Such messages can sound convincing when they include real personal details.
That’s why people should avoid sharing additional financial or identification information with unverified contacts.
SM also advised against clicking suspicious links or opening attachments from unknown sources.
What Private Information Was Leaked From SM Entertainment?
The information released by SM Entertainment indicates that the incident involved several types of personal and business-related records.
The following table summarizes the reported categories.
| Information category | Reported exposure |
|---|---|
| Names | Yes |
| Mobile phone numbers | Yes |
| Residential addresses | Yes |
| Bank account numbers | Yes |
| Resident registration numbers | Yes |
| Department details | Yes |
| Job positions and titles | Yes |
| Contract-related information | Some information |
| Passwords | Not confirmed in the announcement |
| Bubble fan conversations | Not reported as affected |
| Complete employee database | Not established |
One important point is that SM hasn’t published a complete list of affected documents.
The company also hasn’t confirmed that every individual had all the listed information exposed.
For that reason, it’s better to describe the incident as a confirmed personal information breach rather than claim that every employee’s complete private records were leaked.
Why Is This Information Sensitive?
Personal information becomes especially valuable to criminals when several different details are available together.
For example, a scammer who knows someone’s name, phone number, workplace, and other personal details may be able to create a more convincing fraudulent message.
Similarly, information connected to financial accounts can make impersonation attempts more believable.
This is why data protection isn’t only about keeping passwords safe.
Companies must also protect administrative documents, employment records, and confidential contracts.
Were K-Pop Idols’ Private Information and Messages Leaked?
This is one of the biggest questions among K-pop fans.
SM Entertainment manages several well-known artists, and news about a company data breach naturally creates concern about their privacy.
However, readers should distinguish between three different categories:
- Employee personal information.
- Artist-related business and contract information.
- Artists’ private communications and personal accounts.
The company confirmed that certain documents and personal information were leaked. It also mentioned contract-related information.
However, the public announcement doesn’t establish that private conversations, personal photographs, passwords, or private social media messages belonging to specific idols were exposed.
There is currently insufficient verified information to claim that any particular SM artist’s private chats or personal photographs were leaked.
What About EXO, NCT, aespa, and Red Velvet?
Fans may be wondering whether artists from groups such as EXO, NCT, aespa, and Red Velvet were affected.
At present, the public information doesn’t provide a verified artist-by-artist list of affected individuals.
The presence of contract-related information in the reported leak also doesn’t prove that individual artists’ complete contracts or private records were exposed.
Until SM Entertainment or a reliable investigation provides additional details, claims naming particular idols should be treated as unverified.
The important takeaway: A confirmed company data breach doesn’t automatically mean that every artist, employee, or fan has had their personal information exposed.
DearU Data Breach: Is the Bubble App Safe for K-Pop Fans?
DearU’s involvement has become one of the most discussed parts of the SM Entertainment hacking story.
The company operates Bubble, a platform that allows fans to receive artist messages and participate in fan communication services.
Because Bubble is connected to artists and their fan communities, reports of a data breach involving DearU quickly raised concerns.
However, available reporting provides an important clarification: the exposed information was reportedly related to DearU employees, not Bubble users.
This distinction is essential.
Were Bubble Subscribers Affected?
According to reports published on November 8, SM Entertainment said fan information wasn’t leaked in the DearU incident.
Therefore, there is no verified basis for claiming that Bubble subscribers’ private messages or personal account information were exposed in this particular incident.
Nevertheless, users should continue following official security announcements.
They should also:
- Use a strong, unique password.
- Avoid suspicious login links.
- Never share verification codes.
- Check official account notifications.
- Avoid downloading unofficial applications.
- Contact the platform through its official support channels if suspicious activity appears.
These are sensible precautions for any online service.
SM Entertainment’s Official Response to the Cyberattack
SM Entertainment published an official statement on November 8, 2026.
The company acknowledged that an external attacker had accessed internal business systems without authorization and leaked some stored documents.
It apologized for the incident and explained that it was working with relevant authorities to investigate what happened.
The company also outlined several immediate actions.
1. Blocking Unauthorized Access
SM said it blocked the IP addresses and access routes associated with the attack.
This was intended to prevent the attacker from continuing to access the affected systems through the identified routes.
2. Replacing Unauthorized Access Keys
The company also replaced access keys associated with the unauthorized activity.
This is an important security measure because compromised access credentials can create additional risks if they’re not disabled or replaced.
3. Working With Government Authorities
SM confirmed that it was cooperating with government authorities and external specialists.
The investigation is important for identifying how the attacker entered the system, which documents were taken, and whether additional security weaknesses remain.
4. Notifying Affected Individuals
The company said it was identifying the people whose information had been exposed.
It planned to send individual notifications through email or text messages.
This process is important because the leaked information varies between individuals.
5. Improving Internal Security
SM also promised to strengthen internal access controls and security monitoring.
The company said it would investigate the cause and improve its security framework to reduce the possibility of similar incidents.
Why Is the SM Entertainment Hacking Incident So Concerning?
The entertainment industry depends on large amounts of confidential information.
A major agency doesn’t only manage music releases and artist schedules. It also handles employment records, contracts, financial documents, business partnerships, and other sensitive information.
When an attacker gains access to these systems, the potential impact can extend beyond the company’s daily operations.
Employee Privacy Is at Risk
Employees trust their employers to protect personal information.
Names, addresses, phone numbers, and identification numbers aren’t ordinary business details.
They can reveal information that individuals would normally share only with trusted organizations.
Contract Information Can Be Sensitive
Entertainment contracts can contain confidential business arrangements.
The SM announcement confirmed that some information recorded in contracts was among the reported exposed data.
However, the company hasn’t publicly established the exact contents of every affected contract.
It’s therefore too early to determine the full business impact.
Financial Fraud Is a Possible Concern
The exposure of bank account and identification details creates concerns about impersonation and financial scams.
For example, criminals may pretend to represent an employer, financial institution, or business partner.
They may use personal information to make their requests appear legitimate.
This is one reason SM specifically warned about suspicious calls and messages.
How Can Employees and Affected Individuals Protect Their Information?
People who receive an official notification from SM Entertainment or an affected affiliate should carefully review the information provided.
They should avoid assuming that all their personal information was exposed.
Instead, they should confirm the exact categories of information involved.
Here are some practical precautions.
| Potential risk | Recommended action |
|---|---|
| Suspicious phone calls | Don’t share financial or identification details |
| Fake company emails | Verify the sender through official channels |
| Suspicious SMS messages | Avoid unknown links |
| Unexpected payment requests | Confirm directly with the company |
| Unusual bank activity | Contact the bank immediately |
| Identity misuse concerns | Contact the relevant authorities |
| Suspicious account activity | Change affected passwords |
Watch Out for Fake SM Entertainment Messages
Following a major data breach, scammers may try to take advantage of public concern.
For example, a fraudulent message could claim that someone must complete an urgent identity verification process.
Another message might promise compensation for people affected by the incident.
People should be especially careful if a caller or sender asks for:
- Bank passwords.
- One-time verification codes.
- Credit or debit card details.
- Additional identification documents.
- Money to process a compensation request.
Never trust a request simply because the sender knows your name or workplace.
Verify it independently.
Where Can Affected People Get Help?
SM Entertainment listed a dedicated contact email in its official announcement:
privacy@smtown.com
People who suspect they have been affected can contact the company through this channel.
The announcement also referred to South Korea’s Personal Information Dispute Mediation Committee (KOPICO).
Its contact number is 1833-6972.
The company additionally explained that affected individuals may have legal options under relevant provisions of South Korea’s Personal Information Protection Act.
For official information, readers can visit:
Impact on the K-Pop Entertainment Industry
The SM Entertainment data breach has created another important discussion about cybersecurity in the Korean entertainment business.
K-pop agencies work with large networks of employees, artists, production teams, sponsors, contractors, and digital platforms.
This creates a complex information environment.
A company’s security responsibilities don’t end with protecting its public website or official social media accounts.
Internal systems also need strong protection.
K-Pop Agencies Need Stronger Data Protection
Entertainment companies should regularly review:
- Employee access permissions.
- Internal document storage.
- Electronic approval systems.
- Third-party software.
- Authentication procedures.
- Security monitoring.
- Incident response plans.
Not every employee needs access to every company document.
Restricting access according to job responsibilities can reduce unnecessary exposure.
Third-Party Security Is Also Important
The involvement of DearU and Dream Maker has highlighted the importance of protecting information across affiliated companies.
Businesses often share information with subsidiaries and external partners.
If one organization has weaker security practices, it may create risks for the wider business network.
Therefore, regular security assessments should cover both internal systems and important third-party services.
Comparison With Other K-Pop Industry Data Breaches
SM Entertainment isn’t the only major Korean entertainment company to face cybersecurity concerns in 2026.
According to reporting by The Korea Herald, HYBE also experienced incidents involving unauthorized access to business systems and personal information.
The report described separate incidents involving employee and business-related information, as well as security issues involving fan-related services.
However, these incidents should not be treated as identical.
Different companies may experience different types of attacks, different information exposure, and different consequences.
The wider lesson is that cybersecurity is becoming an increasingly important issue for the entire entertainment industry.
For SM Entertainment, the current priority should be completing its investigation, communicating clearly with affected individuals, and demonstrating that its security improvements are effective.
What Happens Next in the SM Entertainment Data Leak Investigation?
The investigation is still an important part of this developing story.
Several questions remain unanswered.
First, how many people were affected?
SM hasn’t publicly confirmed the total number of affected individuals.
Second, how many documents were taken?
The company has confirmed that some documents were leaked but hasn’t published a complete document count.
Third, how did the attacker gain access?
The unauthorized access has been acknowledged, but the precise technical method hasn’t been publicly established.
Fourth, were any additional systems affected?
The company and relevant authorities will need to establish the full scope of the incident.
Fifth, what long-term security changes will be introduced?
SM has promised stronger access controls, monitoring, and security improvements. Further updates will help establish how those commitments are implemented.
These questions matter because the impact of a data breach can’t be fully understood from the initial announcement alone.
For readers following K-pop news, the best approach is to rely on official company announcements and credible news organizations rather than viral posts that claim to reveal unverified private information.
Frequently Asked Questions (FAQs)
1. Did SM Entertainment really get hacked in November 2026?
Yes. SM Entertainment officially confirmed on November 8, 2026, that an external attacker gained unauthorized access to its internal business systems and leaked some stored documents. The reported incident occurred around November 4.
2. What information was leaked from SM Entertainment?
The reported information included names, mobile phone numbers, addresses, bank account numbers, South Korean resident registration numbers, department and job-position details, and some contract-related information. The exact information exposed differs between affected individuals.
3. Were EXO, NCT, aespa, or Red Velvet members affected?
There is no verified public artist-by-artist list confirming which idols were affected. Although SM mentioned contract-related information, this doesn’t establish that specific artists’ private information or personal conversations were leaked.
4. Was the DearU Bubble app hacked?
DearU, the company operating Bubble, experienced an employee-related information leak. However, SM’s explanation indicated that Bubble users’ personal information wasn’t affected. Fans shouldn’t confuse an employee data breach with a confirmed compromise of subscriber accounts.
5. Did SM Entertainment confirm any financial damage?
No secondary damage caused by misuse of the leaked personal information had been confirmed when SM issued its announcement. The company nevertheless warned about possible impersonation, phishing, and financial scams.
6. When did the SM Entertainment data breach happen?
According to the company’s official announcement, the information leak occurred around November 4, 2026. SM publicly acknowledged the incident on November 8.
7. Did SM Entertainment apologize for the data leak?
Yes. The company issued an official apology and said it was taking the incident seriously. It also promised to strengthen internal security monitoring and access controls.
8. How can affected individuals contact SM Entertainment?
SM Entertainment listed the dedicated email address privacy@smtown.com for questions and suspected damage related to the incident. Affected individuals should use verified company contact information rather than suspicious links or phone numbers.
9. Has SM Entertainment revealed how many people were affected?
The company hasn’t publicly disclosed a final total number of affected individuals in the available announcement. It said it was identifying affected people and notifying them individually.
10. Is the SM Entertainment hacking investigation complete?
The investigation was ongoing as of November 9, 2026. SM said it was working with relevant authorities and external specialists to determine the exact circumstances and improve its security systems.
Conclusion: SM Entertainment Faces Serious Questions After Data Breach
The November 2026 cyberattack has become a serious concern for SM Entertainment and its affiliated companies.
The company confirmed that an external attacker accessed internal business systems and leaked documents containing sensitive personal information. The reported exposure included employee identification details, phone numbers, addresses, bank account numbers, and contract-related information.
The involvement of DearU and Dream Maker Entertainment has also increased attention on cybersecurity across the K-pop industry.
However, one important clarification remains: there is currently no verified confirmation that Bubble users’ personal information or specific K-pop idols’ private conversations were leaked.
SM Entertainment has apologized, blocked the identified access routes, replaced unauthorized access keys, and started working with relevant authorities.
The next important step will be completing the investigation and providing clear information to affected individuals.
For now, fans and employees should avoid spreading unverified leak claims and remain alert to phishing messages and fraudulent calls.
The incident is a reminder that protecting personal information must remain a priority for every major entertainment company.
More Info About Kpopbio